Network performance issues can disrupt business operations before users or customers even notice the cause. A Network Operations Centre (NOC) provides centralised visibility into network infrastructure, systems, and connectivity, helping teams monitor performance, identify issues, and maintain availability. Understanding how a NOC works, its core functions, and its benefits helps organisations build more reliable IT operations.
Table of Contents
Key Takeaways
- NOC meaning: A Network Operations Centre provides centralised oversight of network infrastructure, helping organisations maintain reliable connectivity, network availability, and day-to-day IT operations.
- NOC functions: NOC teams monitor network health, detect and troubleshoot incidents, manage performance, support maintenance and recovery, and escalate complex issues to the appropriate technical teams.
- NOC operations: Effective NOC operations follow a continuous cycle of monitoring, alert analysis, incident resolution, escalation, and performance review, supported by monitoring tools, automation, AI, and documented processes.
- NOC value: A well-managed NOC can reduce downtime, improve incident response, provide real-time operational visibility, and create more consistent network management, while requiring investment in people, technology, and processes.
- NOC models: Organisations can use an in-house, outsourced, or hybrid NOC depending on their network complexity, required coverage, internal expertise, operational priorities, and budget.
What Is a NOC and What Does It Stand For?
A NOC, or Network Operations Centre, is a centralised function responsible for managing an organisation’s network and related IT infrastructure. It provides the operational oversight needed to maintain connectivity, manage network resources, resolve technical issues, and support the reliable functioning of critical IT services.
Why Do Organisations Need a NOC?
Organisations need a NOC to maintain visibility and control across their network and infrastructure. A NOC helps teams monitor network devices, identify network performance issues, respond to network incidents, and maintain network uptime. By continuously overseeing the health of the network, NOC staff can address issues before they develop into wider network disruptions or failures.
A NOC also gives organisations a structured way to manage network operations as their infrastructure grows. Instead of relying only on individual network engineers to troubleshoot problems, a dedicated NOC analyst or team can coordinate monitoring, troubleshooting, maintenance, and escalation across the network environment.
Also Read: What Is a SOC Analyst?
Which Industries Rely on NOCs?
NOCs are used across industries where network connectivity, network services, and system availability directly support business operations. Organisations with large or distributed network environments may use an in-house NOC or outsource monitoring through managed NOC services.
Common examples include:
- Banking and financial services: Monitor network infrastructure supporting banking platforms, branches, transactions, and customer services.
- Healthcare: Maintain connectivity between hospitals, clinics, medical systems, and other critical infrastructure.
- Telecommunications: Monitor extensive network systems, network devices, connectivity, and service availability across geographically distributed environments.
- Manufacturing: Support connected production systems, facilities, and operational technology networks.
- Retail and e-commerce: Maintain the network services and connectivity required for stores, payment systems, online platforms, and logistics.
- Government and public services: Monitor network environments that support citizen services, internal systems, and distributed offices.
- Technology and cloud service providers: Oversee complex network and data centre environments where network performance and availability are critical.
- Education: Support connectivity and network services across campuses, institutions, and remote learning environments.
For organisations operating large, distributed, or business-critical infrastructure, a NOC can serve as the nerve centre for modern network operations, helping teams maintain network performance and availability as they scale.
What Does a NOC Do?
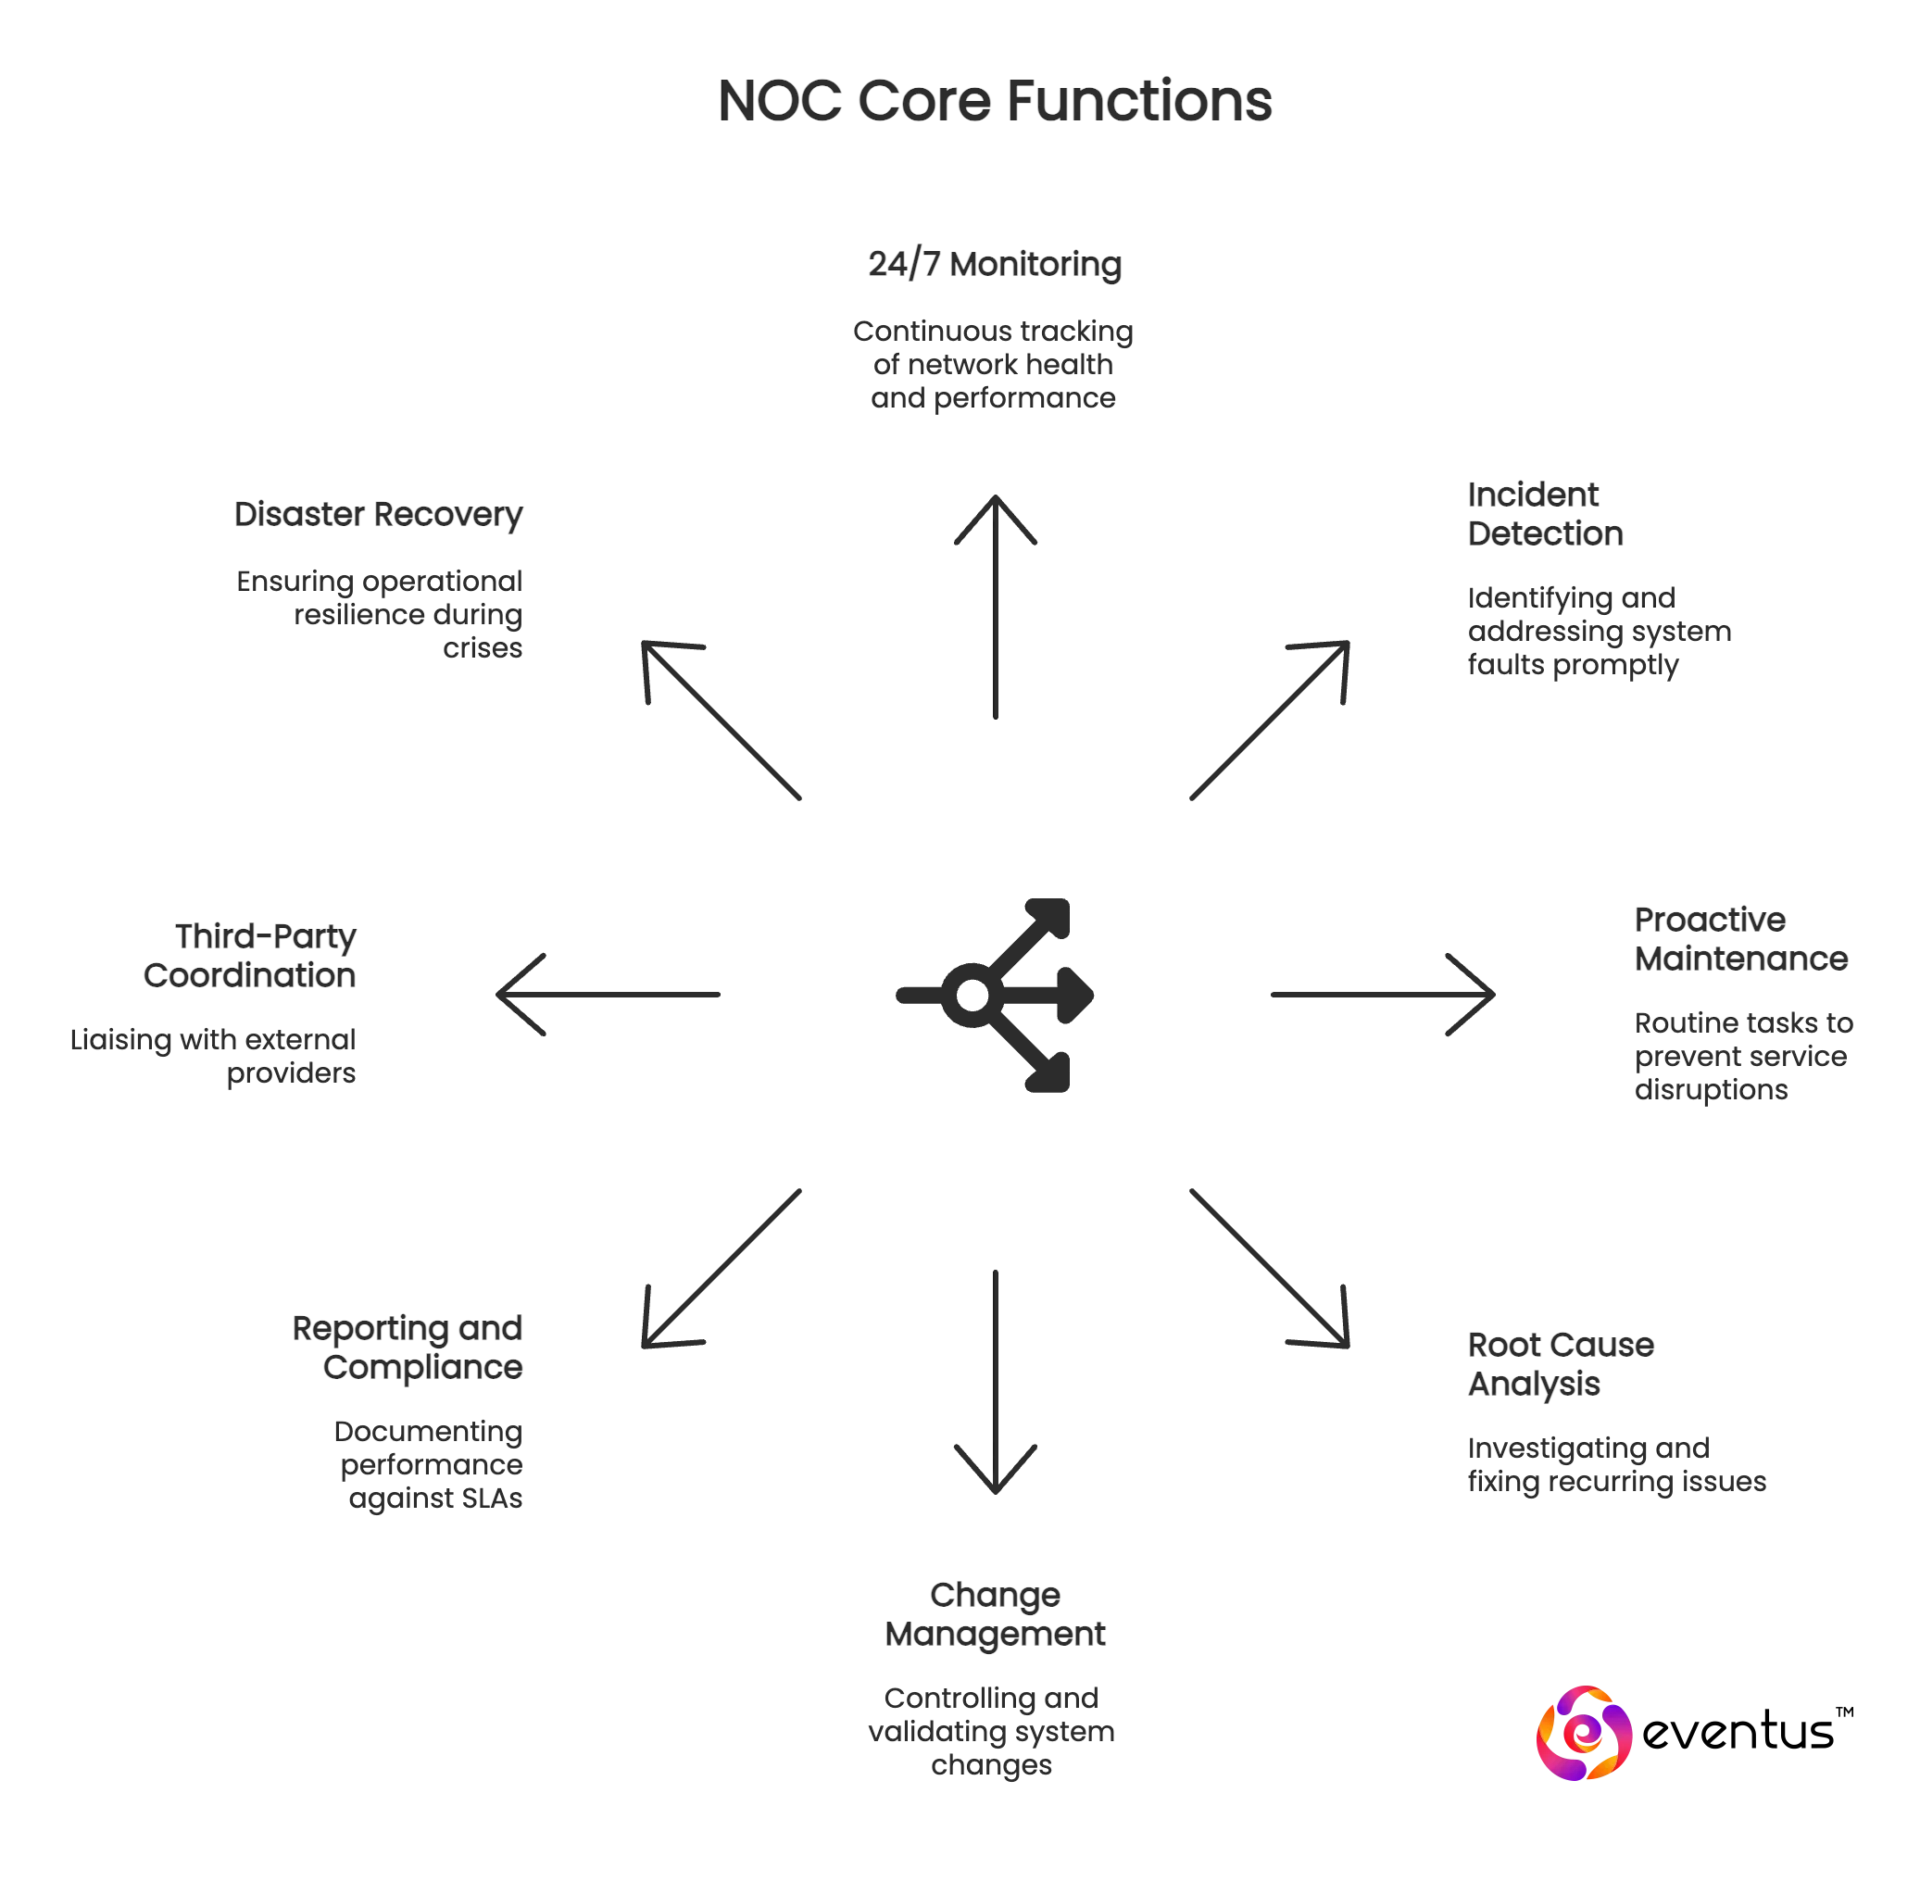
A NOC is responsible for the day-to-day monitoring and management of an organisation’s network and infrastructure. Its responsibilities can include network observability, incident handling, maintenance, security support, performance management, and capacity planning. While the exact scope varies, NOC operations are centred on maintaining reliable network services and supporting business operations.
1. 24/7 Network Monitoring and Alerting
NOC staff continuously monitor network systems, network devices, connectivity, and critical infrastructure using specialised monitoring tools. They track metrics such as availability, latency, bandwidth utilisation, device status, and link health, with alerts generated when predefined thresholds are exceeded. This network observability gives a NOC analyst continuous visibility into the health of the network and helps identify conditions that could affect network uptime.
2. Incident Management, Troubleshooting and Root Cause Analysis
When network incidents occur, NOC staff assess their impact, troubleshoot the underlying issue, and coordinate escalation to network engineers or other specialists when required. Common incidents include connectivity failures, routing problems, device faults, configuration errors, and degraded links. Root cause analysis after resolution helps determine why an incident occurred and reduces the likelihood of recurring network disruptions and failures.
3. Patch Management, Backup and Disaster Recovery
Depending on its operating model, a NOC may coordinate approved patches, maintain network device configurations, monitor backup processes, and support disaster recovery procedures. These activities help keep network and infrastructure components maintained while providing recovery options when equipment fails or critical services are disrupted. Effective recovery planning helps organisations restore network connectivity and essential network services within defined operational requirements.
4. Security Support: Firewalls, Antivirus and Threat Alerts
Network security support may form part of NOC responsibilities, although dedicated security teams such as a Security Operations Centre (SOC) may own threat investigation and response. Depending on the organisation, NOC staff can monitor firewall availability, review relevant security alerts, verify protection systems, and escalate suspicious activity. This makes the NOC an important first line of defense against network-related security and availability issues.
5. Performance Reporting, Optimisation and Capacity Planning
NOCs analyse operational data to evaluate network performance and availability over time, including bandwidth utilisation, latency, packet loss, device availability, and recurring network performance issues. These insights support network optimisation and capacity planning by helping teams identify bottlenecks, overloaded infrastructure, and growing resource requirements before they affect business operations or network uptime.
| Strengthen Your Security Operations
Extend your network operations with continuous security monitoring, threat investigation, and incident response from Eventus Security. |
How Does a NOC Work?
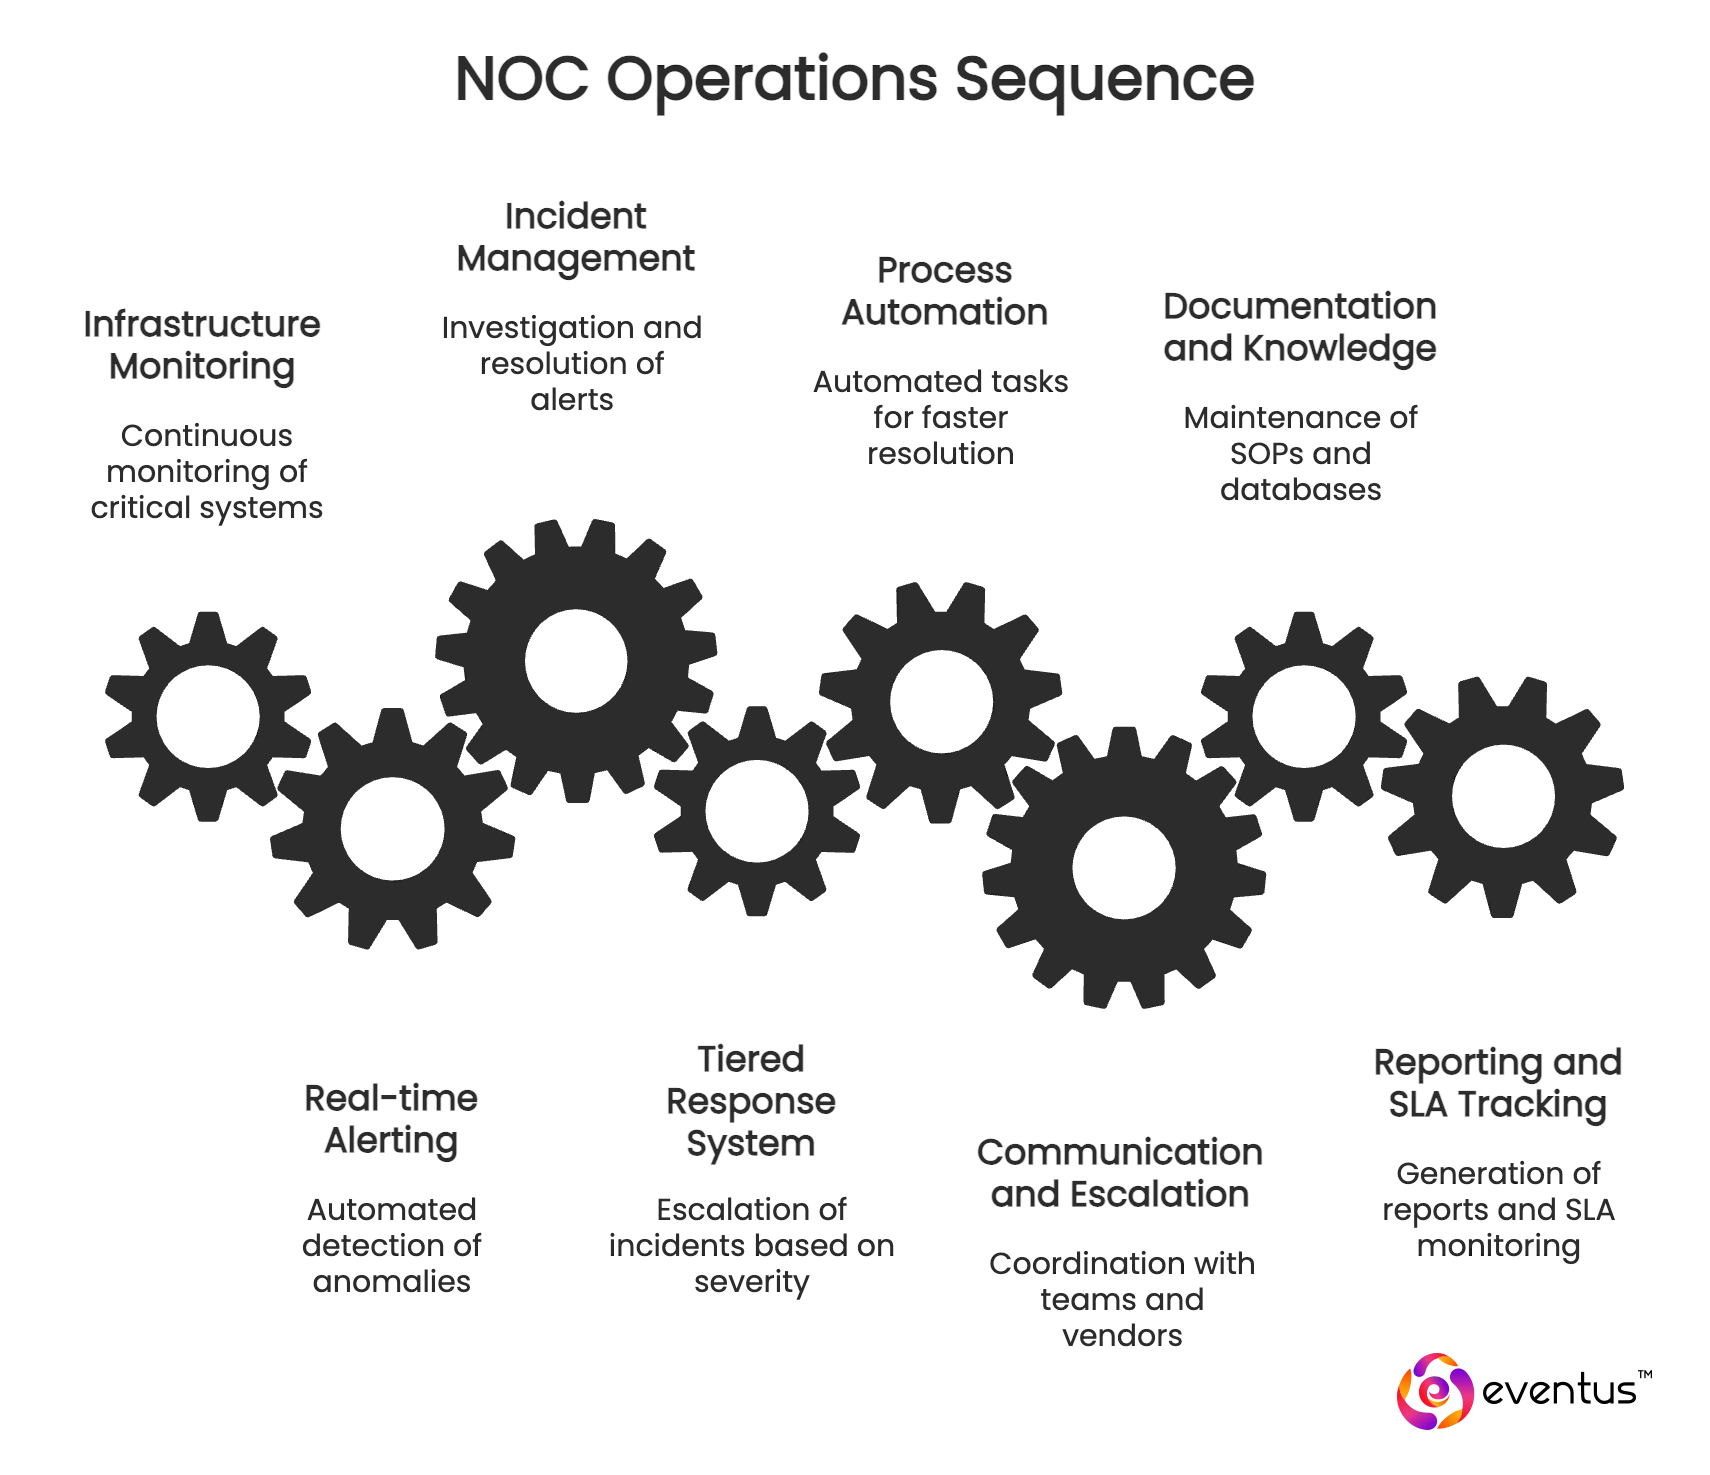
A NOC works through a continuous operational cycle that helps teams maintain network availability and resolve infrastructure issues. The process typically involves monitoring network conditions, identifying deviations from normal performance, diagnosing the affected systems, applying corrective actions, and escalating issues that require specialised network expertise.
1. Monitoring Network Infrastructure
A NOC continuously collects operational data from routers, switches, firewalls, servers, links, wireless controllers, and other network infrastructure. Monitoring platforms track conditions such as device availability, latency, packet loss, bandwidth utilisation, interface status, and service availability across offices, data centres, cloud environments, and distributed locations.
2. Identifying Network Conditions That Require Attention
Monitoring tools generate alerts when network conditions move outside defined thresholds, such as a device becoming unavailable, bandwidth utilisation increasing significantly, or latency and packet loss exceeding acceptable levels. NOC analysts review these conditions to determine their severity, scope, and potential effect on network services.
3. Diagnosing and Correcting Network Problems
After identifying an issue, NOC staff use monitoring data, device logs, configuration information, connectivity tests, and recent infrastructure changes to determine the likely cause. Depending on the issue and their authorised responsibilities, they may perform corrective actions such as restarting a service, addressing an approved configuration problem, or rerouting traffic.
4. Escalating Complex Network Issues
Issues that cannot be resolved within the NOC's defined responsibilities are escalated to network engineers or other specialised teams. Escalation procedures typically consider technical complexity, affected infrastructure, business impact, and required expertise, ensuring that more complex network problems reach the appropriate team without unnecessary delays.
5. Using Network Monitoring Tools and Automation
Modern NOCs use network monitoring platforms, infrastructure monitoring tools, log management systems, ticketing platforms, configuration management tools, and IT service management systems to support daily operations. Automation can handle repetitive tasks such as health checks, ticket creation, alert routing, and predefined remediation actions, while AI can help identify unusual network conditions and prioritise operational issues for NOC staff.
Organisations that need additional operational support can also work with a managed security provider alongside their existing IT and network teams. Eventus Security combines continuous monitoring, security analytics, threat investigation, and incident response to help teams maintain visibility across their environment and respond to issues that require specialised security expertise.
How Is a NOC Different From a SOC and a Help Desk?
A NOC, SOC, and help desk may all respond to IT-related issues, but their responsibilities are different. The NOC focuses on network availability and infrastructure operations, the SOC handles cybersecurity threats, and the help desk provides direct technical support to users.
NOC vs SOC
The main difference between a NOC and SOC is what each team is responsible for protecting and maintaining. A NOC focuses on the availability and performance of network infrastructure, whereas a SOC focuses on identifying and responding to cybersecurity threats.
| Area | NOC | SOC |
| Primary focus | Network and infrastructure operations | Cybersecurity operations |
| Main objective | Maintain network performance and availability | Detect and respond to security threats |
| Monitors | Network devices, connectivity, bandwidth, and infrastructure health | Security events, endpoints, identities, and threat indicators |
| Typical incidents | Outages, connectivity failures, latency, and device issues | Malware, suspicious activity, unauthorised access, and data compromise |
| Core personnel | NOC analysts and network engineers | Security analysts, threat hunters, and incident responders |
NOC vs Help Desk
The NOC and help desk may both become involved when an employee or customer experiences an IT problem, but they address different layers of the issue. The help desk focuses on user assistance, while the NOC manages underlying network and infrastructure conditions.
| Area | NOC | Help Desk |
| Primary focus | Network and infrastructure operations | User support and IT service requests |
| Main objective | Maintain network availability and connectivity | Resolve user-facing technical issues |
| Typical issues | Network outages, device failures, and connectivity problems | Password resets, software issues, access requests, and device assistance |
| Primary users | IT and infrastructure teams | Employees, customers, and end users |
| Escalation role | Escalates complex infrastructure issues to specialised teams | Escalates network, security, application, or infrastructure issues when required |
How Do NOC, SOC and Help Desk Work Together?
These teams can operate as connected functions within an organisation’s IT operations. The help desk may identify a widespread connectivity issue and escalate it to the NOC, while the NOC can involve the SOC when an issue appears security-related. The SOC may also involve the NOC when a security incident affects network infrastructure, allowing the teams to coordinate investigation, containment, and service restoration.
What Are the Benefits and Challenges of a NOC?
A NOC can give organisations a centralised function for monitoring and managing network operations, but maintaining one also requires the right people, processes, technology, and investment. Its value depends on how effectively the NOC team turns real-time network visibility into timely action without creating unnecessary operational overhead.
Key Benefits of a NOC
A well-managed NOC gives organisations continuous oversight of network operations and a structured way to maintain availability, investigate issues, and support business-critical services.
- Centralised network management: A NOC team can centralise monitoring and operational oversight across network devices, infrastructure, connectivity, and services instead of managing each environment separately.
- Reduced downtime: Continuous monitoring helps NOC technicians identify failures and performance degradation early, allowing issues to be addressed before they result in prolonged service disruption.
- Faster incident response: Defined workflows allow technicians and NOC engineers to assess incidents, prioritise their impact, and involve the right technical teams without unnecessary delays.
- Real-time operational visibility: Monitoring platforms provide real-time information about network health, availability, traffic, and device status, helping teams make decisions based on current conditions.
- Consistent network operations: Documented procedures and best practices give the NOC team a repeatable approach to monitoring, troubleshooting, escalation, and maintenance.
- Better coordination with security teams: A NOC can work alongside a security operations center when network events have potential security implications, helping coordinate network management and security operations.
Common Challenges of NOC
Operating a NOC can become difficult when infrastructure expands faster than the team’s ability to monitor and manage it. Common challenges include excessive alerts, staffing costs, shortages of experienced NOC engineers and technicians, and maintaining consistent visibility across on-premises, cloud, and multi-cloud environments.
- Alert fatigue: Large numbers of low-priority or duplicate alerts can overwhelm NOC technicians, making it harder to identify events that genuinely require immediate attention.
- Operational cost: An in-house NOC requires investment in monitoring platforms, infrastructure, staffing, training, and 24/7 operational coverage where required.
- Skill shortages: Experienced NOC engineers need knowledge across networking, cloud infrastructure, monitoring, troubleshooting, and incident response, making skilled resources difficult to recruit and retain.
- Multi-cloud complexity: Monitoring network connectivity, workloads, and dependencies across multiple cloud providers alongside on-premises infrastructure can make visibility and troubleshooting more complicated.
- Tool and process integration: A NOC may need to connect monitoring, ticketing, automation, configuration, and incident management systems so that information can move efficiently between teams.
- Maintaining consistent operations: As the network environment changes, the NOC must regularly update monitoring rules, escalation procedures, documentation, and best practices to remain effective.
What Are the Best Practices and KPIs for Running a NOC?
Effective NOC operations require standardised procedures as well as measurable performance targets. Best practices help the NOC team work consistently across shifts and incidents, while KPIs provide measurable evidence of how well the network operations function is performing.
Best Practices for Running a NOC
A NOC should establish repeatable processes for common operational tasks and maintain accurate information that technicians can use during incidents. The following practices help maintain consistency across NOC operations:
- Maintain detailed runbooks: Document step-by-step procedures for common network issues, maintenance activities, escalation paths, and incident response scenarios.
- Keep network documentation current: Record network topology, device details, dependencies, configurations, service ownership, and known issues so technicians can investigate incidents efficiently.
- Standardise shift handovers: Record active incidents, pending actions, planned changes, unresolved alerts, and important network conditions before transferring responsibility to the next shift.
- Define escalation procedures: Establish clear criteria for when an issue should move from a NOC technician to a NOC engineer, specialist team, or external provider.
- Review procedures regularly: Update runbooks and documentation after major incidents, infrastructure changes, and process improvements to keep them aligned with the current network environment.
Also Read: SOC Best Practices for Modern Cyber Defense
Key Metrics of a NOC
NOC KPIs should measure both how quickly teams identify problems and how effectively they restore affected services. A focused set of metrics can help management evaluate operational performance without relying on incident volume alone:
- Mean Time to Detect (MTTD): Measures the average time between the occurrence of a network incident and its detection by the NOC.
- Mean Time to Resolve (MTTR): Measures the average time required to restore normal service after a network incident is identified.
- Network uptime: Measures the percentage of time that a network service or infrastructure component remains available during a defined period.
- SLA compliance: Measures whether agreed targets for availability, response times, and resolution times are being achieved.
- Incident volume: Tracks the number of network incidents handled over a defined period and can help identify recurring operational problems.
- Repeat incidents: Measures how often similar issues recur and can indicate whether root causes are being addressed effectively.
Should You Choose an In-House, Outsourced or Hybrid NOC?
The right NOC model depends on the organisation’s network infrastructure, internal expertise, operational coverage, and growth plans. An in-house model provides greater control, an outsourced model brings external expertise and managed coverage, while a hybrid approach divides responsibilities between internal teams and an external provider.
1. In-House NOC
An in-house NOC is operated by the organisation’s own NOC team and provides direct control over the company’s network, monitoring processes, and operational decisions. It can be suitable for organisations with complex or sensitive infrastructure that need dedicated internal expertise, but building a strong NOC requires investment in skilled technicians, monitoring technology, shift coverage, and ongoing training.
2. Outsourced NOC
An outsourced NOC uses a specialist provider to perform agreed network and infrastructure monitoring, incident handling, and operational support. This model can help organisations ensure network uptime without building a full internal management centre, while providing access to experienced NOC personnel, established NOC best practices, and the ability to scale operations as the organisation’s network grows.
3. Hybrid NOC
A hybrid NOC combines internal network operations with outsourced capabilities, allowing an organisation to retain control over critical systems while using external expertise for monitoring, after-hours coverage, or specialised tasks. It can be effective for distributed environments, including cloud, data centre, and satellite network environments, where flexible coverage is needed to strengthen the defence against network disruptions.
Does Your Business Actually Need a NOC?
Not every organisation needs a dedicated NOC from the beginning. The need becomes more apparent when network operations become too large, distributed, or business-critical for basic IT monitoring to manage effectively. The following indicators can help determine whether your organisation is ready for a more structured NOC approach.
Five Signs You Have Outgrown Basic IT Monitoring
Basic monitoring can show that something is wrong, but a growing network may require dedicated people and processes to investigate and resolve issues consistently. Consider a NOC when:
- Network incidents are increasing: Your IT team is spending more time investigating recurring network issues, outages, and connectivity problems.
- Downtime affects business operations: Network failures are disrupting applications, locations, customer services, or employee productivity.
- Your infrastructure is becoming distributed: Managing offices, data centres, cloud environments, remote users, or satellite network environments is making network visibility more difficult.
- Internal teams cannot provide continuous coverage: Network issues occurring outside normal working hours remain unresolved until the internal IT team becomes available.
- Monitoring generates alerts without enough response capacity: Your tools identify network conditions, but there is not enough time or expertise to investigate, prioritise, and resolve them consistently.
NOC Readiness Checklist for Indian Businesses
For Indian businesses, NOC readiness should be assessed against operational scale, network complexity, service availability requirements, and internal IT capabilities. A business may be ready for a NOC if it can answer “yes” to several of these questions:
- Do you need continuous visibility into your organisation’s network?
- Are network disruptions affecting critical business services?
- Does your IT team struggle to respond to network incidents outside business hours?
- Do you operate across multiple offices, data centres, cloud environments, or locations?
- Are network monitoring and escalation processes currently inconsistent?
- Do you have defined requirements for network uptime and service availability?
- Do your network operations require specialised NOC technicians or engineers?
- Is your organisation expanding faster than your existing IT monitoring capabilities?
Which NOC Model Fits Your Budget and Team Size?
The most suitable NOC model depends on the organisation’s available IT resources, network complexity, required coverage, and budget rather than employee count alone. Smaller teams may benefit from outsourced NOC services when they lack dedicated network expertise, while larger organisations with complex infrastructure may prefer an in-house or hybrid model to retain greater operational control while using external support where needed.
| Need Additional Security Operations Support?
If your internal NOC or IT team needs additional security monitoring and incident response capabilities, explore how Eventus Security can complement your existing operations. |
How Can Eventus Security Complement NOC Operations?
NOC teams focus on maintaining network availability, performance, and reliable infrastructure operations, while security events may require specialised monitoring and investigation. Eventus Security can complement existing NOC and IT teams through managed security operations, combining continuous security monitoring, AI-correlated alerts, threat hunting, and incident response. This allows organisations to strengthen security oversight while their NOC continues managing network and infrastructure operations.
Eventus Security’s Key Security Operations Capabilities:
- 24/7 Security Monitoring: Continuously monitors security events across the environment to help identify activity that may require investigation or response.
- AI-Correlated Alert Analysis: Correlates security alerts to help identify significant events and reduce the volume of individual alerts that security teams need to review.
- Threat Hunting and Investigation: Security analysts investigate suspicious activity and proactively hunt for potential threats across the monitored environment.
- Incident Response: Supports the investigation and response process when security incidents affect an organisation’s systems or infrastructure.
- Managed Security Operations: Combines security technology with human analyst expertise to provide ongoing security operations support alongside existing NOC, IT, and security teams.
Speak to Eventus Security to discuss managed security operations and incident response support for your organisation.
FAQs
1. What should you look for when choosing a NOC service provider?
Look for proven network monitoring capabilities, 24/7 coverage, experienced NOC staff, defined escalation procedures, strong incident response, clear SLAs, reporting, security practices, and the ability to support your organisation’s existing network infrastructure and future growth.
2. What should a managed NOC service include?
A managed NOC service should typically include 24/7 network and infrastructure monitoring, alert management, incident detection, troubleshooting, escalation, performance monitoring, reporting, maintenance coordination, and defined SLAs. The exact scope should match your organisation’s infrastructure, availability requirements, and operational needs.
3. How much does it cost to outsource NOC services in India?
The cost of outsourced NOC services in India varies based on infrastructure size, monitoring scope, coverage hours, service levels, technologies, and required expertise. Providers may charge through fixed monthly fees, per-device pricing, or customised service agreements based on requirements.
4. What is a NOC engineer?
A NOC engineer, short for Network Operations Centre engineer, is an IT professional who monitors network health, resolves complex incidents escalated by NOC analysts, performs root cause analysis, and supports maintenance so that network disruptions are fixed before they affect business operations.